Vendor Risk Management
Meet Our Team
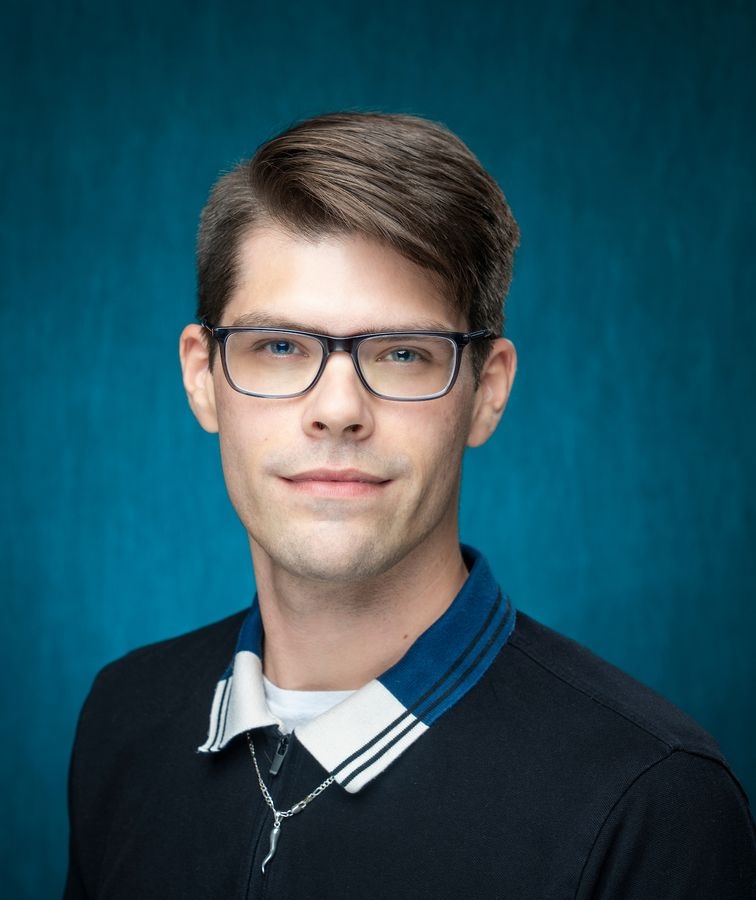
Sebastian S Floryan
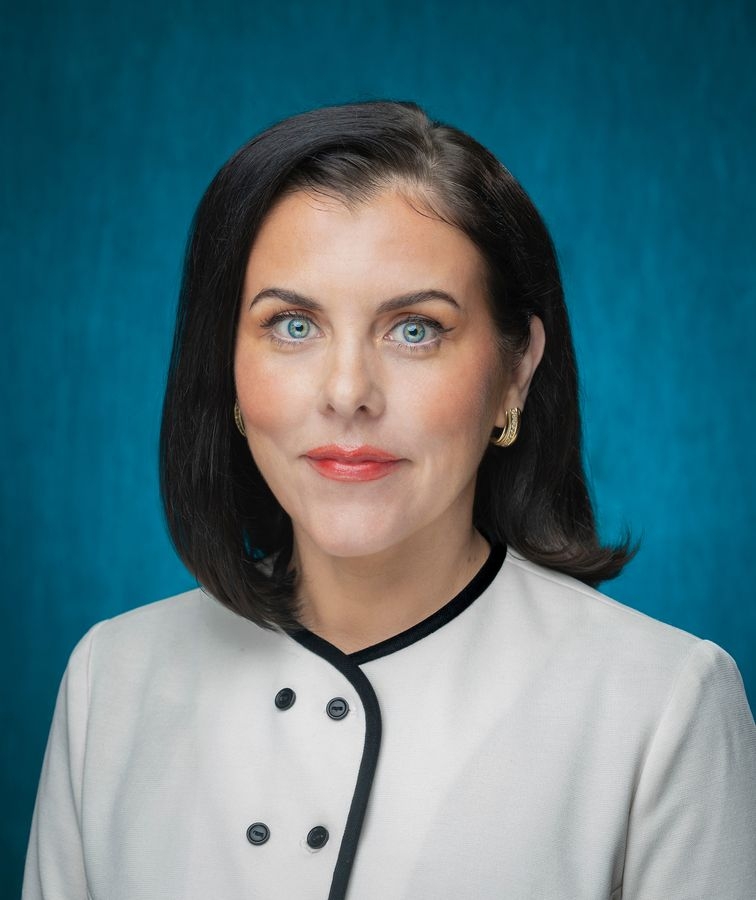
Allison M. Streuter
Vendors are identified when departments submit a purchase requisition through uShop (access via mySeaport) or an installation or integration request through the myTAC Portal.
Prior to submitting your request, we encourage you to review the Questions to Consider section as you evaluate solutions for your department or business needs.
Our team will contact both your department and the vendor to collect the information needed to complete the assessment.
We review the vendor's security and privacy documentation and prepare an ITS risk assessment report for the relevant Data Steward(s).
The Data Steward(s) who are responsible for the overall protection and management of the identified data will receive the ITS risk assessment report and address any items of concern with our team or the requesting department.
After the review is complete and the appropriate approvals have been received by Data Steward(s) and university stakeholders, the request will be approved by ITS.
If data protection concerns or other key risks are identified, our team will share the assessment findings with your area for review, evaluation and planning.
Any acquisition, whether paid or for free, of information technology solutions as defined in UNCW 07.400.01 and 05.151, is required to be reviewed through the IT vendor risk management process. This includes:
- All purchases
- All installs
- All use of free solutions
For specific detail on how to initiate the review process with the ITS Vendor Risk Management team, reach out via email at VRM@uncw.edu.
Once a purchase is entered into uShop and received budget approval, ITS and Purchasing receive the requisition at the same time. This facilitates a concurrent workflow step where ITS conducts its independent review for IT and related considerations while Purchasing is able to address state and university procurement requirements.
Requisitions in uShop that are routed through the ITS workflow require both ITS and Purchasing approval. Once both approvals are entered, and any additional approvals that are required, the Purchase Order will be generated.
A formal IT risk assessment is required for any information technology solution, whether paid or free, that meets one or more of the following criteria:
- Stores, processes, transmits, or otherwise utilizes university data classified as highly sensitive or ultra-sensitive, as defined by the UNCW 01.250 Data Governance and Management Policy and the UNCW Data Classification Matrix.
- Integrates with university systems, including but not limited to those that store, process, transmit, or otherwise utilize sensitive, confidential, and/or regulated data, as prescribed by applicable law, regulation, or policy.
- Is acquired through the competitive procurement process, including requests for proposals, bids, quotes, or any formal acquisition channel.
- Is identified by ITS or the designated Data Steward as requiring assessment due to potential risk factors, even if it does not explicitly meet the above thresholds.
The following factors may impact the amount of time an IT risk assessment takes:
- Providing ITS a direct point of contact with the vendor versus a general help@... email address.
- Reviewing and negotiating contracts and special terms.
- Availability of vendor staff to provide up-to-date security and privacy documentation.
- Negotiation of any non-disclosure agreements (NDAs) prior to accessing vendor's confidential business information.
Yes. The IT Vendor Risk Management team actively maintains the Campus Software List. This list is non-exhaustive and does not capture every software title that has been previously reviewed or approved by ITS for purchase or installation. Updates are made monthly.
If you or your department would like to verify if a specific piece of software or other IT solution has been approved for purchase previously, please reach out and our team will review available resources.
Campus is reminded that all requests to purchase or install software, whether free or paid, are required to be reviewed prior to purchase or installation in accordance with UNCW's 07.400.01 and 05.151 policies.
Software purchases, including those intended to be paid via departmental P-Card, must be submitted through uShop for both ITS and Purchasing review and approval. Departments must use the Software/IT-Related Solution Form located on the uShop homepage when submitting related requests.
Software installations, updates, and license transfers must be submitted through the myTAC portal and will be reviewed by the appropriate team in ITS, as necessary, to facilitate the request.